Enterprise Documentation
Governance & Compliance
for Azure DevOps Wiki
Transform your existing Azure DevOps Wiki into a governed, audit-ready documentation platform — without migration, duplication, or external systems. Activate governance instantly, page by page.
Designed for compliance-driven organizations
What is Contextra Labs?
Contextra Labs is established in Dubai, United Arab Emirates, and publishes five extensions: two for Azure DevOps and three for Atlassian Jira and Confluence.
Governance for Wiki, the extension described on this page, adds approval workflows, an audit trail and page ownership to Azure DevOps Wiki. The others are Contextra Draw, RTL Pro for Confluence, File Field for Jira and Secure Field for Jira.
Azure DevOps Wiki Governance
Built for Compliance Teams
Everything your audit-driven organization needs to control, track, and prove documentation compliance — built directly on top of your existing Wiki.
Structured Governance Workflow
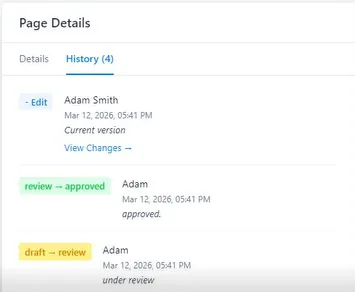
Draft → In Review → Approved lifecycle with required reviewers, SLA tracking, mandatory change summaries, and clear ownership assignment.
Audit & Compliance Traceability
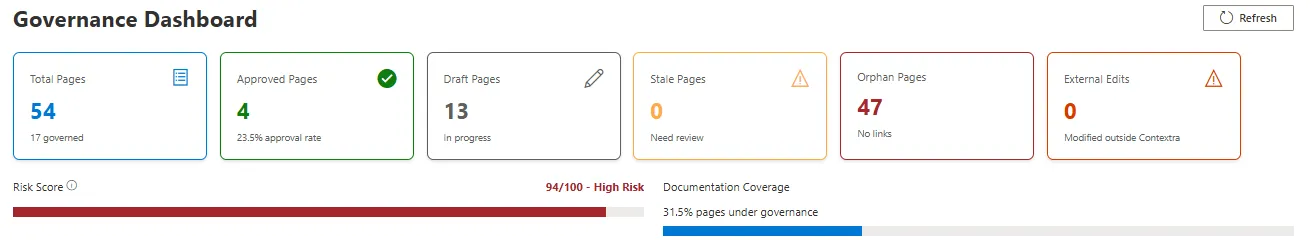
Immutable version history, append-only audit log, approval traceability, and documentation aging dashboard for ISO 27001, SOC 2 evidence collection.
Draw.io Diagrams Inside Wiki Pages
Native Draw.io editing inside Azure DevOps Wiki pages. Diagrams versioned alongside content, fully governed and audit-traceable. For diagrams in work items, repos and pull requests, see Contextra Draw.
Secure by Design
Uses Azure DevOps native identity. No external backend, no external storage, no custom RBAC. All data stays inside your Azure environment.
Instant Setup — No Migration Required
Works directly on top of your existing Azure DevOps Wiki. No page migration, no repository changes, no duplication of content, no restructuring required.
Install the Extension
Available directly from the Azure DevOps Marketplace. Installation takes minutes.
Enable Governance Per Page
Selectively activate governance on any Wiki page. No restructuring required.
Assign Reviewers & Owners
Define authorized reviewers using users or Azure DevOps Security Groups.
Govern & Audit Instantly
Approval workflows, audit logs, and compliance visibility activate immediately.
Security Audit Ready: Since this is a client-side extension with no external backend, it typically clears internal IT security reviews much faster than SaaS-based alternatives.
Built for Compliance & Audit Driven Organizations
Contextra Draw — draw.io beyond the Wiki
Governance covers your Wiki pages. If your team also needs draw.io diagrams in work items, repository files and pull requests, that is our second extension.
Ready to Govern Your
Azure DevOps Wiki?
Start your 30-day full-feature trial — no credit card required. Experience every governance tool from day one.